Advertisements
Top weekly article
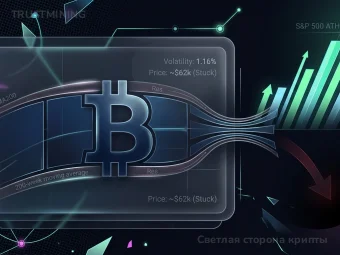
Светлая сторона крипты
Ветры зимы в криптосфере
Почему биткоин застрял на месте, пока фондовый рынок бьет рекорды

A replay attack occurs when an attacker reuses a previously captured and valid message, signature, or transaction to cause an operation to be executed again.
A digital signature proves that a particular set of data was signed by the corresponding key, but a signature alone does not necessarily guarantee that the message can only be used once. A protocol must include context, uniqueness, and state information to prevent unintended reuse.
Blockchain replay protection may use transaction inputs, nonces, network identifiers, chain identifiers, or other fields. These mechanisms distinguish a new operation from one that has already been processed.
Replay risks are particularly well known when one blockchain splits into two networks after a hard fork. If the transaction formats and signature rules do not sufficiently distinguish the chains, a transaction valid on one network may potentially be replayed on the other.
Replay protection is therefore part of transaction-format design, digital-signature design, and the rules of the specific blockchain.
Popular models

Brands


Fluminer

ElphaPex

Ebang

Canaan

Todek

Bitdeer

iPollo

Baikal

StrongU

VolcMiner

MicroBT

Lucky Miner

Jasminer

Auradine

Innosilicon

IceRiver

Hummer Miner

Holic

Heatbit

Goldshell

FusionSilicon

Bitaxe

Bitfily

Digital Shovel

Dayun

Bolon Miner

Braiins

BW

Halong Mining

Bitfury

Spondoolies

PinIdea

Pantech

Obelisk

DragonBall Miner

FFMiner

ForestMiner

GMO miner