Advertisements
Top weekly article
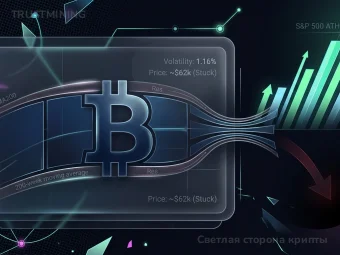
Светлая сторона крипты
Ветры зимы в криптосфере
Почему биткоин застрял на месте, пока фондовый рынок бьет рекорды

Phishing is an attack in which an attacker creates a false appearance of trust in order to make a user reveal sensitive information or perform a dangerous action. In cryptocurrency, common targets include seed phrases, private keys, passwords, and authentication codes.
Phishing can use fake exchange websites, wallet interfaces, emails, messaging apps, advertisements, or social-media links. The malicious resource may closely imitate the design and behavior of the legitimate service.
Common warning signs
- unexpected requests to urgently verify an account;
- a domain name that resembles the legitimate service but contains subtle differences;
- requests for a seed phrase or private key;
- offers of free tokens or unusually high returns in exchange for connecting a wallet;
- pressure based on account suspension or supposed security incidents.
A legitimate cryptocurrency service should not normally require users to reveal a private key or seed phrase for routine wallet access. These secrets are central to private-key security and seed-phrase security.
Phishing frequently overlaps with social engineering. Technical account protections should therefore be combined with careful verification of websites, messages, applications, and the identity of people requesting sensitive actions.
Popular models

Brands


Fluminer

ElphaPex

Ebang

Canaan

Todek

Bitdeer

iPollo

Baikal

StrongU

VolcMiner

MicroBT

Lucky Miner

Jasminer

Auradine

Innosilicon

IceRiver

Hummer Miner

Holic

Heatbit

Goldshell

FusionSilicon

Bitaxe

Bitfily

Digital Shovel

Dayun

Bolon Miner

Braiins

BW

Halong Mining

Bitfury

Spondoolies

PinIdea

Pantech

Obelisk

DragonBall Miner

FFMiner

ForestMiner

GMO miner